
Research · · verified August 21, 2026
What Should Access Recertification Check for Offshore Editorial Roles?
Research on proportionate access reviews for offshore researchers, writers, editors, and publishing coordinators.
*August 21, 2026*
Research question
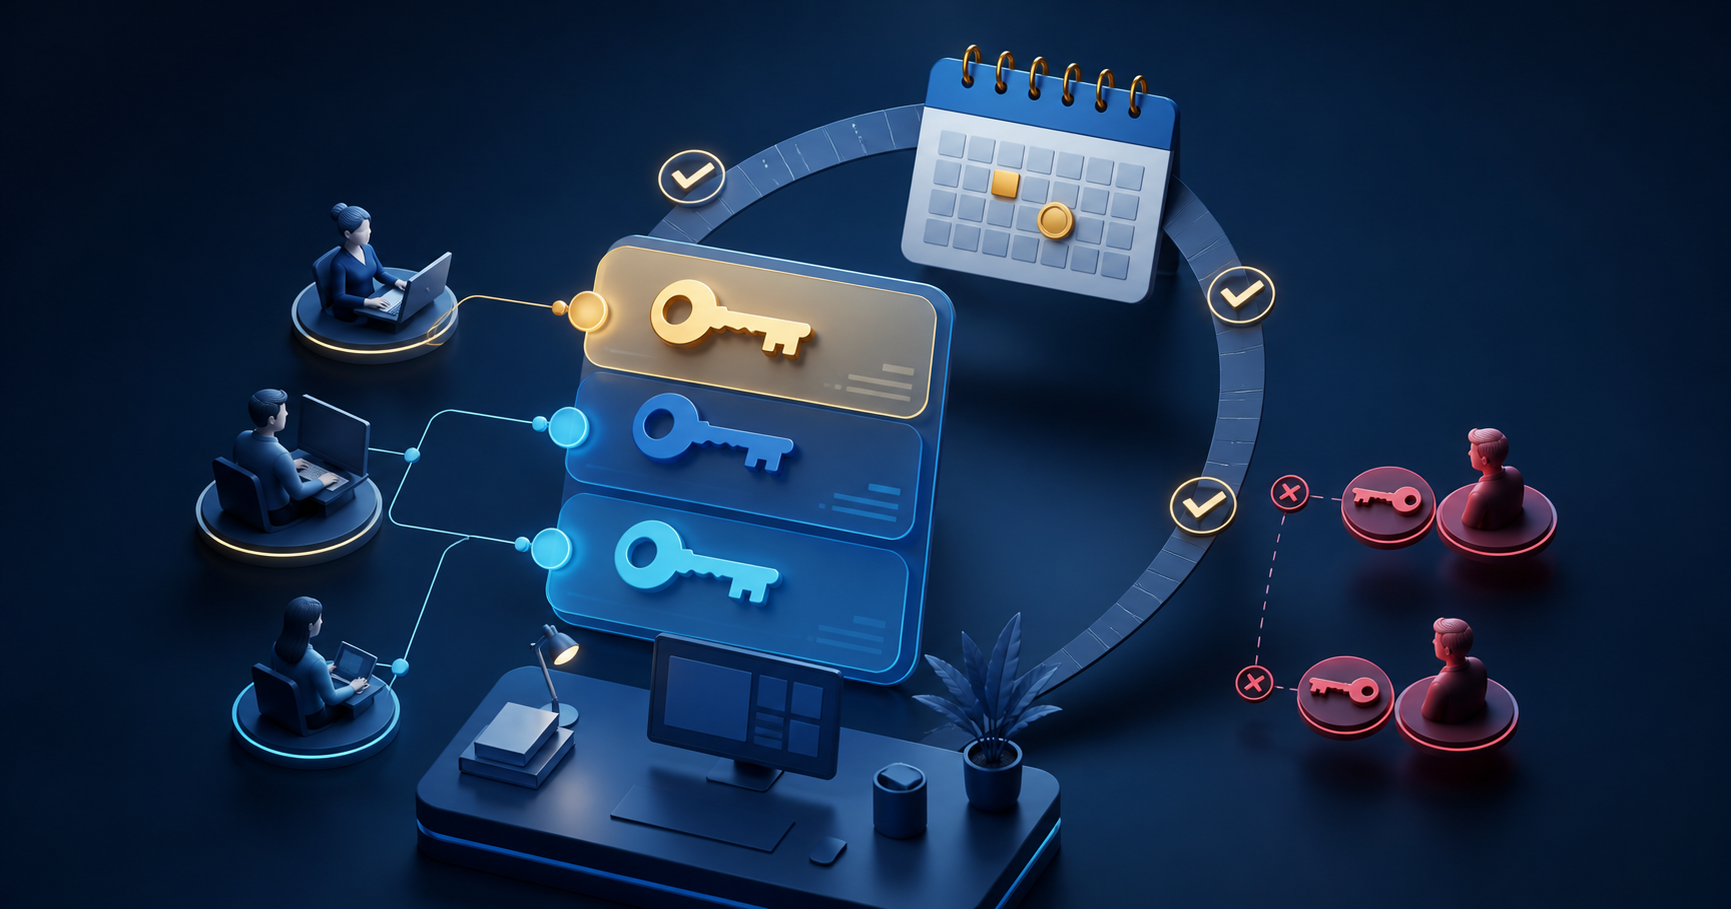
What should a recurring access recertification check when offshore editorial roles touch research sources, drafts, analytics, or publishing controls? The question is narrower than whether remote work is secure. It asks whether a manager can show that access still matches current responsibility, that exceptions have an owner, and that removal is possible when work changes. Offshore Resourcing needs this distinction because article routines can expand gradually: a researcher receives a shared folder, a reviewer receives an approval permission, and a coordinator later inherits a publishing account.
Methodology and evidence scope
This is a qualitative documentary review. I compared the access-control principles in the public NIST, CISA, CIS, ISO, OWASP, GAO, ICO, and Australian Cyber Security Centre materials listed below, then translated recurring concepts into questions for an offshore editorial routine: role need, permission purpose, scope, ownership, review trigger, exception expiry, and removal evidence. I tested the questions against three illustrative work states, evidence preparation, editorial review, and publication coordination, to see whether each state could be assigned a proportionate permission boundary. The examples are analytical scenarios, not observations of a named team or an audit sample. The evidence can support a control model and identify what a manager should inspect; it cannot establish the security of any particular account, vendor, platform, or company.
Role to permission mapping
Begin with the work, not the application. A researcher may need to read approved sources and store evidence, while a writer needs draft access and an editor needs review comments. A publishing coordinator may require a controlled release action, but that does not imply authority to change a brief or approve a sensitive claim. Mapping permissions to tasks exposes accidental bundling. The map should name the accountable manager, the system owner, the purpose, the maximum sensitivity, and the condition that ends access.
Recertification questions
Every review should ask: does the person still perform the role; is the permission used for that role; is the scope narrower than the whole workspace; has the source or project changed; are shared credentials prohibited; is an exception documented; and who can remove access? A yes-or-no result is not enough if the reviewer cannot see the evidence. Record the decision, the reviewer, the date, the next review point, and the reason for any retained exception. Avoid collecting unnecessary personal information.
Evidence and review timing
Timing should follow risk and change, not a ritual calendar alone. Review after a role change, project close, system change, or suspected misuse. Routine access can receive a periodic review when risk is lower. High-impact publishing controls require tighter ownership because an incorrect release can affect public copy. The recertification record should distinguish “not used recently” from “not needed,” since inactivity may reflect a seasonal responsibility. Offshore teams should be able to escalate uncertain cases to the authorized system or security owner.
Least privilege in editorial work
Least privilege is often misunderstood as giving every role the smallest possible number of buttons. In editorial operations it means giving enough access to complete an assigned task while separating preparation, review, approval, and release where practical. A person can prepare an article without being able to publish it. A reviewer can flag a claim without changing the underlying source register. The exact separation depends on the platform, but the decision right should remain visible even when technical controls are limited.
Exceptions and failure paths
An exception may be justified by a temporary absence, a system limitation, or a time-sensitive publishing need. It should not become a permanent second path. Record why the exception exists, who accepted it, what compensating review applies, and when it expires. If an account cannot be removed promptly, the escalation should name the system owner and interim safeguard. This is a management control, not a public marketing claim. Public copy should never disclose credentials, internal permission structures, or customer-specific access details.
What the evidence can show
A good review can show whether permission purpose, owner, scope, and decision history are observable. It can identify orphaned access, role drift, stale exceptions, and unclear removal paths. It cannot show that misuse never occurred, that a person is trustworthy, or that a framework guarantees compliance. Nor can a recertification replace identity proofing, monitoring, secure configuration, or legal review. Separating those conclusions prevents a narrow access check from being advertised as a complete security program.
A proportionate pilot
Pilot the design on one recurring article stream with three role types: evidence preparation, editorial review, and publication coordination. Inventory access, compare it to assigned work, and ask a second authorized reviewer to inspect the decisions. Count unresolved exceptions, not only removed permissions. Interview the role owner about false positives, because excessive removal can interrupt legitimate work and encourage unsafe workarounds. Revise the map before expanding it to other teams. The pilot should produce decisions and owners, not a decorative score.
Limitations
This analysis uses public security and control guidance, not an audit of any Offshore Resourcing system. Platforms differ in their ability to separate permissions, record approvals, and export logs. Local employment, privacy, contractual, and sector-specific rules may add requirements. A review can also be complete on paper while the source data is wrong or a shared account masks the real user. The proposed questions therefore support management review and specialist escalation; they do not constitute certification or legal advice.
Conclusion
Access recertification for offshore editorial roles should test continuing role need, permission purpose, scope, ownership, exception expiry, and removal evidence. The evidence supports a role-based, change-aware review with stronger separation around publishing decisions. It does not support the claim that a periodic checklist makes a content operation secure. For Offshore Resourcing, the next defensible step is a bounded pilot that distinguishes research, review, and release rights and routes unresolved cases to the system owner before the article routine grows more complex.
Sources
- NIST Cybersecurity Framework 2.0
- NIST SP 800-53 access control
- CISA Identity and Access Management
- CIS Controls v8
- ISO/IEC 27001 overview
- NIST Digital Identity Guidelines
- OWASP access control guidance
- GAO Standards for Internal Control
- ICO access control guidance
- Australian Cyber Security Centre access control
Related Research
How Much Evidence Survives an Offshore Editorial Handoff?
A research review of evidence retention when offshore researchers, writers, and reviewers work across recurring article cycles.
Can Review-Queue Sampling Reveal Quality in Offshore Article Publishing?
An evidence-led study of how representative sampling can expose review risk in recurring offshore editorial work.
Testing Reproducibility in Offshore Access Reviews
A bounded research design for examining access-review reproducibility in distributed operations without overstating causal evidence.